Artificial Intelligence (AI) is no longer a futuristic concept; it’s an integral part of our present, reshaping industries, economies, and daily lives. As AI systems become more sophisticated and ubiquitous, so too grows the imperative for robust governance. The year 2026 is poised to be a pivotal moment, with several significant AI regulatory changes expected to solidify, impacting everything from data privacy to ethical deployment. Businesses and developers worldwide must anticipate and adapt to these shifts to ensure compliance, foster innovation responsibly, and maintain public trust. This comprehensive guide delves into the five biggest regulatory changes for AI in 2026, offering recent updates and insider knowledge to help you navigate this evolving landscape.
Anúncios
The Accelerating Pace of AI Regulation
The rapid advancement of AI has caught many regulatory bodies off guard. Historically, technology has moved faster than the laws designed to govern it. However, the unique capabilities and potential societal impacts of AI – particularly concerning privacy, bias, accountability, and security – have spurred governments and international organizations into accelerated action. The goal is not to stifle innovation but to channel it responsibly, creating a framework that protects individuals and fosters a level playing field for businesses.
Understanding the nuances of these impending AI regulatory changes is crucial for any organization leveraging AI. Non-compliance can lead to hefty fines, reputational damage, and legal battles. More importantly, proactive engagement with these regulations can be a competitive advantage, demonstrating a commitment to ethical AI and building trust with customers and stakeholders.
Anúncios
1. The EU AI Act: Setting a Global Benchmark for Responsible AI
One of the most anticipated and impactful pieces of legislation is the European Union’s AI Act. While much of it is expected to be fully implemented and enforceable by 2026, its influence is already being felt globally. The EU AI Act adopts a risk-based approach, categorizing AI systems into different risk levels – from unacceptable to minimal – with corresponding regulatory requirements.
Key Provisions and Implications:
- Unacceptable Risk AI: Systems deemed to pose an unacceptable risk to fundamental rights (e.g., social scoring by governments, manipulative AI) will be banned. This sends a strong signal about the ethical boundaries of AI deployment.
- High-Risk AI: This category includes AI systems used in critical sectors like healthcare, law enforcement, education, employment, and critical infrastructure. These systems will face stringent requirements, including conformity assessments, risk management systems, human oversight, data governance, cybersecurity measures, and transparency obligations. Companies deploying high-risk AI will need robust internal processes to ensure continuous compliance.
- Limited and Minimal Risk AI: Most AI systems will fall into these categories, with fewer regulatory burdens. However, transparency obligations for systems interacting with humans (e.g., chatbots) will still apply.
Recent Updates and Insider Knowledge:
Recent negotiations have refined the scope of high-risk AI, with a particular focus on general-purpose AI (GPAI) models. The Act now includes specific provisions for these foundational models, requiring them to meet certain safety and transparency standards, especially if they pose systemic risks. This expansion acknowledges the growing power and potential impact of large language models and other sophisticated AI systems. Companies developing or deploying GPAI will need to pay close attention to these evolving requirements, which may include rigorous testing, model evaluations, and reporting on energy consumption. The ‘innovation sandboxes’ proposed within the Act aim to provide a controlled environment for testing novel AI systems, balancing innovation with regulatory compliance.
The EU AI Act is expected to have an extraterritorial effect, similar to GDPR. Any company, regardless of its location, that provides AI systems or services to users within the EU will likely need to comply. This makes it a de facto global standard, compelling businesses worldwide to align their AI strategies with its principles. Preparing for the EU AI Act means investing in robust AI governance frameworks, conducting thorough risk assessments, and ensuring transparent documentation of AI models and their performance.
2. Enhanced Data Governance and Privacy Frameworks for AI
Data is the lifeblood of AI. However, the collection, processing, and use of vast datasets by AI systems raise significant privacy concerns. By 2026, we anticipate a global trend towards strengthening data governance frameworks specifically tailored for AI, building upon existing privacy laws like GDPR and CCPA.
Key Provisions and Implications:
- AI-Specific Data Protection: Expect new regulations or amendments to existing ones that address how AI systems handle personal data, especially in terms of data minimization, purpose limitation, and the right to explainability for automated decisions.
- Synthetic Data and Anonymization: Increased focus on the responsible creation and use of synthetic data and advanced anonymization techniques to train AI models without compromising individual privacy. Regulations may mandate specific standards for these practices.
- Data Provenance and Quality: Emphasis on ensuring the quality, integrity, and provenance of data used to train AI models. This is critical for mitigating bias and ensuring fair and accurate AI outputs.
Recent Updates and Insider Knowledge:
Several jurisdictions, including the US and UK, are exploring AI-specific data protection guidelines. In the US, while a comprehensive federal AI law is still nascent, individual states are advancing their own privacy legislation, many of which include provisions relevant to AI. The UK’s Data Protection and Digital Information Bill, for instance, seeks to create a more flexible data protection regime post-Brexit, but with a continued emphasis on ethical AI and data use. The concept of ‘data trusts’ or ‘data cooperatives’ is gaining traction, where individuals collectively control their data and decide how it’s used by AI systems, potentially becoming a regulated model for data sharing.
Companies will need to implement more sophisticated data governance strategies that not only comply with general data protection laws but also address the unique challenges posed by AI. This includes detailed data mapping, impact assessments for AI-driven data processing, and clear consent mechanisms for data used in AI training. The ability to demonstrate transparent and responsible data handling will be paramount.
3. AI Accountability and Liability Frameworks
As AI systems become more autonomous and capable of making decisions with significant real-world consequences, questions of accountability and liability become central. Who is responsible when an AI system makes a mistake, causes harm, or perpetuates bias? By 2026, we expect clearer legal frameworks to address these complex issues.
Key Provisions and Implications:
- Product Liability for AI: Existing product liability laws may be updated to specifically cover AI systems, defining the responsibilities of developers, deployers, and users. This could lead to a shift in how AI products are designed, tested, and marketed.
- Attribution of Harm: Regulations will aim to establish clearer rules for attributing harm caused by AI, considering factors like data quality, algorithm design, human oversight, and system updates.
- Mandatory Insurance: For certain high-risk AI applications, mandatory insurance schemes might be introduced to cover potential damages or liabilities.
- Algorithmic Audits: The requirement for regular, independent algorithmic audits to verify fairness, transparency, and robustness of AI systems will likely become more prevalent, providing a mechanism for accountability.
Recent Updates and Insider Knowledge:
The European Commission has already put forward proposals for a new AI Liability Directive, aiming to modernize liability rules for digital products and AI. This directive seeks to ease the burden of proof for victims of AI-caused harm, especially in complex cases where identifying the exact cause is difficult. Other nations are watching closely, with discussions in the US on whether to adapt existing tort law or create entirely new legal categories for AI liability. There’s a growing consensus that a multi-stakeholder approach to accountability is needed, involving developers, deployers, regulators, and even users. The concept of ‘explainable AI’ (XAI) will be crucial here, as the ability to understand an AI’s decision-making process will directly impact liability assessments.
Businesses will need to implement robust internal governance structures that clearly define roles and responsibilities for AI development and deployment. This includes detailed record-keeping of AI system design, training data, performance metrics, and human intervention points. Legal teams will need to be well-versed in emerging AI liability doctrines to advise on risk mitigation and insurance strategies.
4. International Standards and Harmonization Efforts for AI
AI is a global phenomenon, and its regulation cannot be confined to national borders. By 2026, we expect to see intensified efforts towards international cooperation and the development of harmonized standards for AI, driven by organizations like the OECD, UNESCO, and the G7/G20.
Key Provisions and Implications:
- Interoperable Regulatory Frameworks: The goal is to create common principles and standards that allow for easier cross-border deployment of AI systems, reducing regulatory fragmentation and compliance burdens for international businesses.
- Ethical AI Guidelines: Global bodies will continue to develop and promote shared ethical guidelines for AI development and deployment, covering areas like fairness, transparency, human-centricity, and environmental sustainability.
- Technical Standards: Collaboration on technical standards for AI, including data formats, interoperability, testing methodologies, and security protocols, will be critical for ensuring consistency and reliability across different AI systems and jurisdictions.
Recent Updates and Insider Knowledge:
The OECD’s Principles on AI have already served as a foundational document for many national AI strategies, emphasizing responsible stewardship of trustworthy AI. UNESCO has also adopted a Recommendation on the Ethics of Artificial Intelligence, providing a global normative instrument. The G7 and G20 are actively discussing common approaches to AI governance, particularly concerning generative AI and its societal implications. The UK’s proposed ‘pro-innovation’ approach aims to avoid a single, overarching AI law, instead empowering existing regulators with sector-specific guidance, but this approach will still need to align with international norms to facilitate global trade and collaboration.
For multinational corporations, tracking these international harmonization efforts is paramount. Adopting best practices that align with global consensus can future-proof AI deployments and simplify compliance across different operating regions. Engaging with industry consortia and standards bodies will be key to influencing these developments and staying ahead of the curve.
5. Sector-Specific AI Regulations and Professional Standards
Beyond broad legislative frameworks, 2026 will likely see a proliferation of sector-specific AI regulatory changes. Industries with particularly sensitive data or high-stakes applications – such as healthcare, finance, automotive, and defense – will develop tailored regulations and professional standards to address their unique challenges.
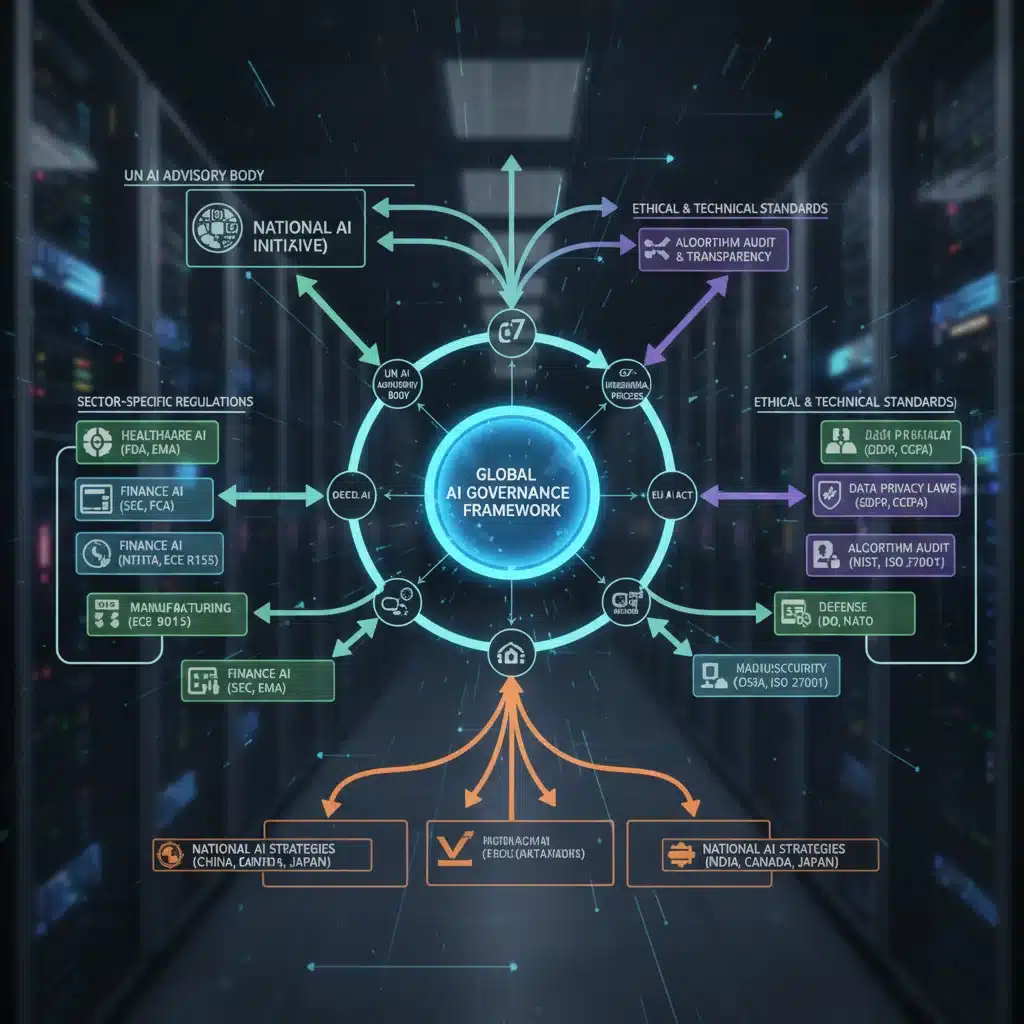
Key Provisions and Implications:
- Healthcare AI: Regulations will focus on the safety, efficacy, and clinical validation of AI in diagnostics, drug discovery, and patient care, potentially requiring specific certifications or oversight bodies.
- Financial Services AI: Emphasis on fairness, explainability, and bias mitigation in AI used for credit scoring, fraud detection, and algorithmic trading, along with strict cybersecurity requirements.
- Autonomous Systems (e.g., Self-Driving Cars): Detailed regulations on testing, safety protocols, liability in accident scenarios, and ethical considerations for decision-making in critical situations.
- Professional Codes of Conduct: Professional bodies (e.g., for doctors, lawyers, engineers) may introduce specific codes of conduct for the ethical use of AI within their professions, outlining responsibilities and best practices.
Recent Updates and Insider Knowledge:
The FDA in the US is actively developing regulatory pathways for AI-powered medical devices, focusing on ‘Software as a Medical Device’ (SaMD) and addressing issues like continuous learning algorithms. The European Banking Authority (EBA) and European Securities and Markets Authority (ESMA) are also issuing guidelines for AI adoption in finance, particularly concerning risk management and consumer protection. In the automotive sector, ISO standards for AI safety (e.g., ISO 21448 for Safety of the Intended Functionality, SOTIF) are gaining traction and may become legally mandated in certain regions. There’s also a growing call for AI ‘licensing’ or certification for professionals developing and deploying AI in critical sectors, similar to engineering or medical licenses.
Businesses operating in these regulated sectors will need to integrate AI compliance into their existing regulatory frameworks. This means collaborating closely with industry-specific regulators, participating in relevant working groups, and investing in specialized expertise to navigate the complex interplay of general AI laws and sector-specific requirements. The ‘human in the loop’ principle will be particularly emphasized in these high-stakes applications, ensuring appropriate human oversight and intervention capabilities.
Preparing Your Organization for the Future of AI Regulation
The landscape of AI regulatory changes by 2026 will be dynamic and multifaceted. Proactive preparation is not just about avoiding penalties; it’s about building a resilient, ethical, and innovative AI strategy. Here are actionable steps organizations can take:
1. Establish an AI Governance Framework:
Develop a clear internal framework that defines roles, responsibilities, and processes for AI development, deployment, and oversight. This should include policies on data privacy, algorithmic fairness, transparency, and accountability.
2. Conduct AI Risk Assessments:
Regularly assess your AI systems for potential risks, including bias, privacy violations, security vulnerabilities, and societal impacts. Categorize your AI applications based on risk levels and prioritize mitigation strategies.
3. Invest in Explainable AI (XAI) and Transparency:
Prioritize the development and use of AI models that are inherently more transparent and explainable. Document your AI models’ design, training data, performance, and decision-making processes thoroughly.
4. Implement Robust Data Governance:
Strengthen your data governance practices, focusing on data quality, provenance, anonymization techniques, and consent management. Ensure your data pipelines are auditable and compliant with evolving privacy regulations.
5. Foster a Culture of Ethical AI:
Educate your teams – from developers to leadership – on ethical AI principles and regulatory requirements. Encourage a culture where ethical considerations are integrated into every stage of the AI lifecycle.
6. Monitor Regulatory Developments:
Stay continuously informed about new legislation, guidelines, and international standards related to AI. Engage with industry associations and legal experts to understand the implications for your specific sector and operations.
7. Engage with Stakeholders:
Collaborate with regulators, policymakers, academics, and civil society organizations. Providing input on emerging regulations can help shape practical and effective policies that foster responsible innovation.
Conclusion: Navigating the AI Regulatory Horizon
The year 2026 marks a significant turning point in AI governance. The confluence of the EU AI Act, enhanced data privacy laws, clearer accountability frameworks, international harmonization efforts, and sector-specific regulations will fundamentally reshape how AI is developed, deployed, and used globally. For businesses, this is not merely a compliance exercise but an opportunity to embed trust, ethics, and responsibility at the core of their AI strategies.
By proactively addressing these anticipated AI regulatory changes, organizations can not only mitigate risks but also unlock new opportunities for innovation, build stronger customer relationships, and contribute to the responsible advancement of artificial intelligence. The future of AI is not just about technological prowess, but about our collective ability to govern it wisely and ethically. Staying informed, adaptable, and committed to responsible AI practices will be the hallmarks of success in this new regulatory era.